Manage access and permissions with ACLs
ACLs are an older, less powerful method of defining access to Object Storage buckets and objects. You can apply ACLs to buckets, and to objects in some cases. With ACLs, there are two generalized modes of access: setting your buckets and possibly your objects to be either private or public.
This is the legacy processYou should define access to Object Storage resources in a bucket policy.
ACLs in Cloud Manager
These sections cover how to apply ACLs using Cloud Manager.
The granular permissions available in Cloud Manager
| Level | Permission | Description |
|---|---|---|
| Bucket | Private | Only you can list, create, overwrite, and delete objects in this bucket. Default |
| Bucket | Authenticated Read | All authenticated Object Storage users can list objects in this bucket, but only you can create, overwrite, and delete them. |
| Bucket | Public Read | Everyone can list objects in this bucket, but only you can create, overwrite, and delete them. |
| Bucket | Public Read/Write | Everyone can list, create, overwrite, and delete objects in this bucket. This is not recommended. |
| Object | Private | Only you can download this object. Default |
| Object | Authenticated Read | All authenticated Object Storage users can download this object. |
| Object | Public Read | Everyone can download this Object. |
Bucket-level ACLs in Cloud Manager
Existing buckets and any new bucket created in Cloud Manager have a default ACL permission setting of Private.
-
Access Cloud Manager.
-
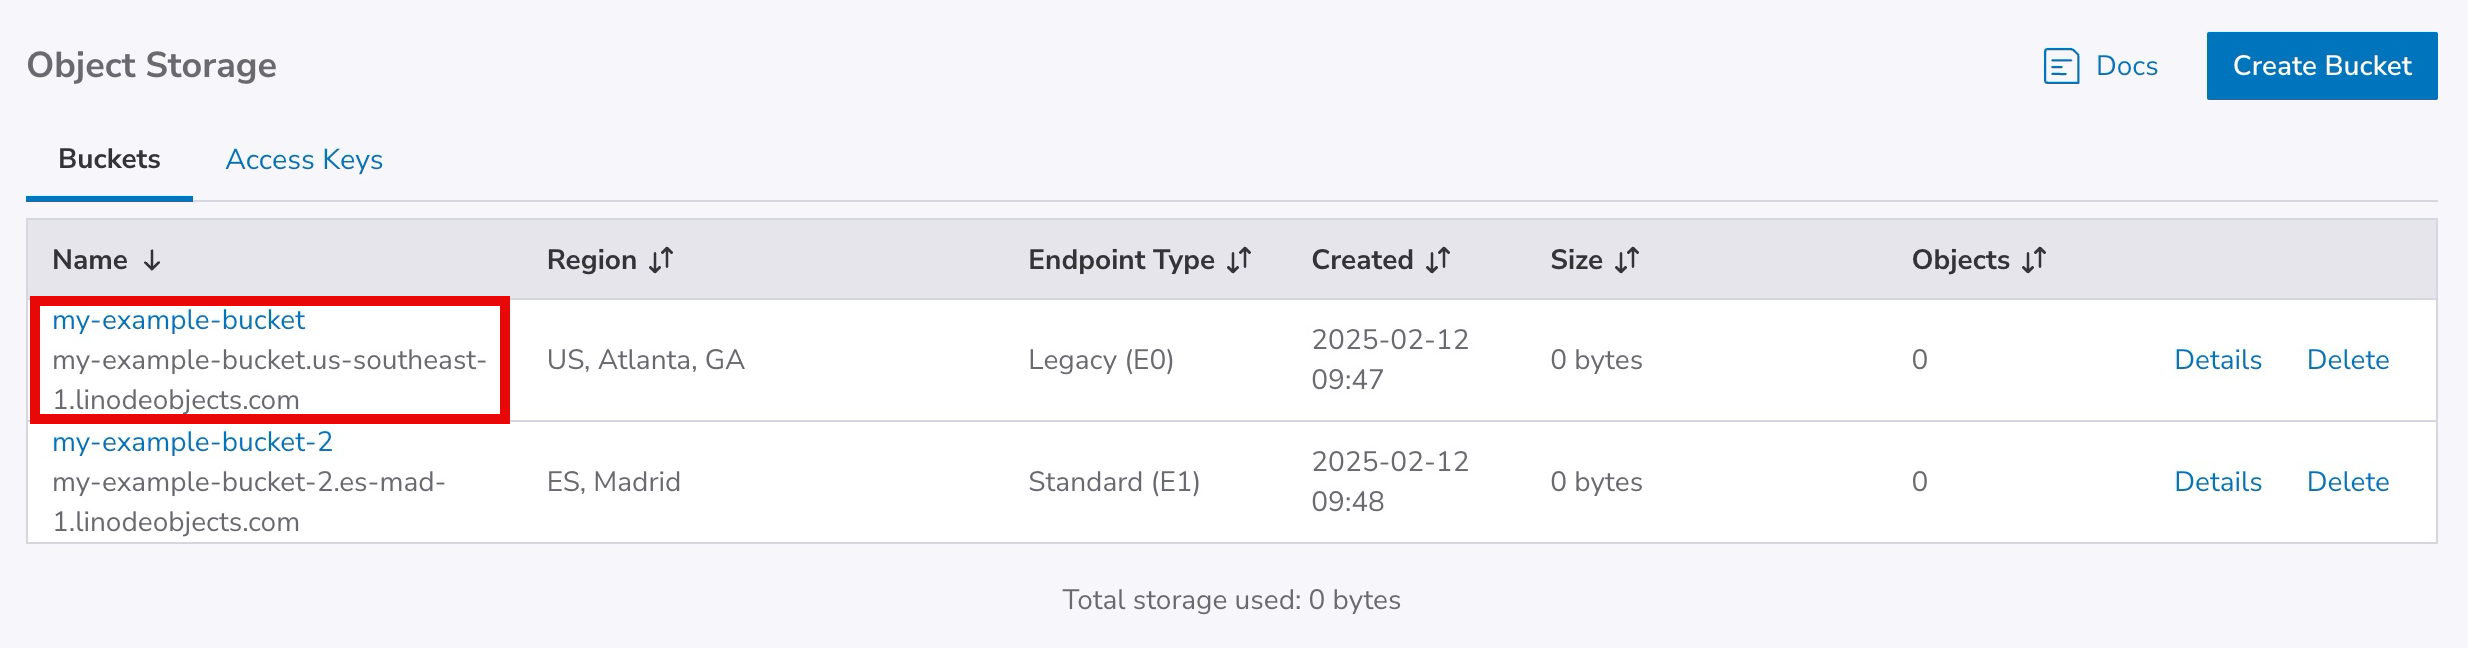
Select Object Storage in the sidebar, and then select the desired bucket.
-
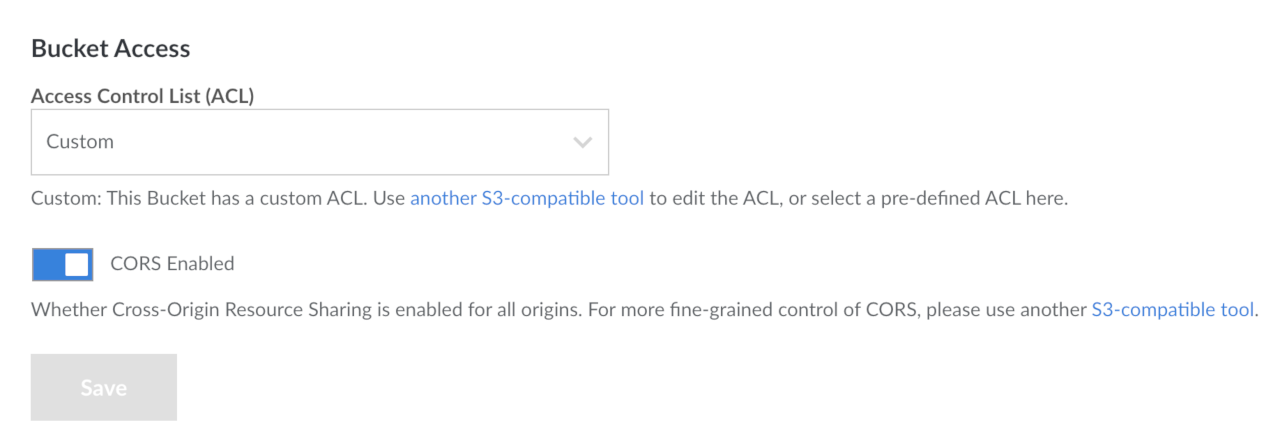
Select the Access tab.
-
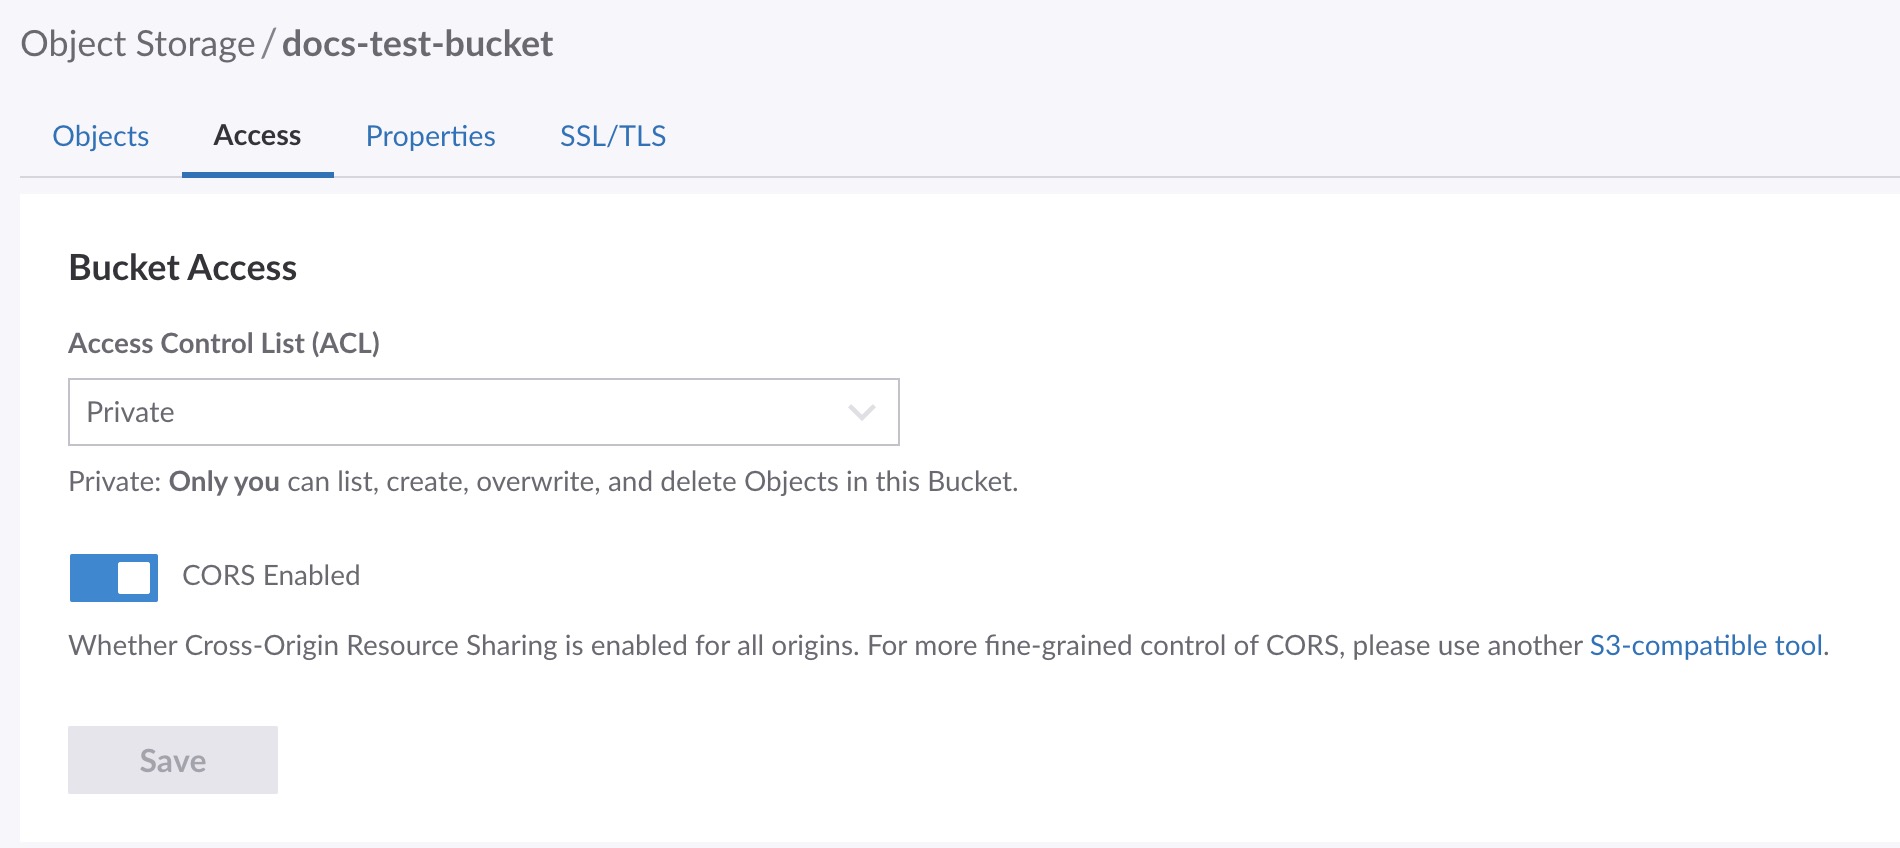
Set these options:
-
Access Control List (ACL). Select the bucket-level permission you want.
-
CORS. Cross-Origin Resource Sharing (CORS) is a security mechanism offered by most browser applications that controls how one domain's web page can request data from a different domain. If enabled, these requests are supported.
CORS is enabled by default on all existing buckets and on all new E0 and E1 endpoints. CORS is not available for E2 and E3 endpoints. See the Endpoint types topic for more information.
-
-
Click Save.
Object-level ACLs in Cloud Manager
E2 and E3 endpoints don't support object-level ACLs.
Existing objects and any new objects created in Cloud Manager have a default ACL permission setting of Private.
-
Access Cloud Manager.
-
Select Object Storage from the sidebar, and then select the bucket that holds the target objects.
-
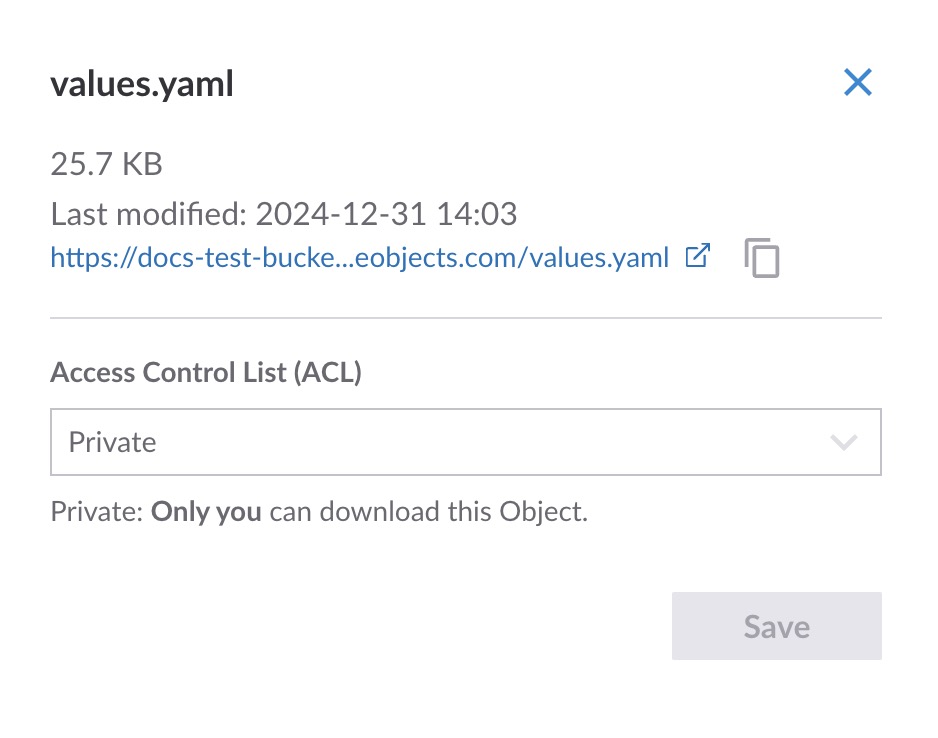
Select the desired object to edit its ACL settings.
-
In the Access Control List (ACL) drop-down, select the object-level permission you want.
-
Click Save.
ACLs with s3cmd
With s3cmd, you can set a bucket's access level:
-
Public. This command sets the bucket to "public." The bucket and its contents are downloadable over the public internet. (This is not recommended)
s3cmd setacl s3://acl-example --acl-public -
Private. This command sets the bucket to "private." The bucket and its contents are blocked from public access over the internet. (Only you will be able to access the bucket and its contents.)
s3cmd setacl s3://acl-example --acl-private
The granular permissions available with s3cmd
There are additional, more granular permissions you can apply through s3cmd:
| Permission | Description |
|---|---|
| read | Users can list objects within a bucket. |
| write | Users can upload objects to a bucket and delete objects from a bucket. |
| read_acp | Users can read the ACL currently applied to a bucket. |
| write_acp | Users can change the ACL applied to the bucket. |
| full_control | Users have read and write access over both objects and ACLs. |
Set a permission
To apply granular permissions for a specific user with s3cmd, use the following setacl command with the --acl-grant flag:
s3cmd setacl s3://<acl-example> --acl-grant=<PERMISSION>:<CANONICAL_ID>Set the <variable> values, excluding the < >:
<acl-example>Set this to the name of the target bucket and the object, if necessary.<PERMISSION>Set this to the desired granular permission<CANONICAL_ID>. Set this to the canonical identifier for the user sho will receive the permissions.
Revoke a permission
To revoke a specific permission, you can use the setacl command with the acl-revoke flag:
s3cmd setacl s3://<acl-example> --acl-revoke=<PERMISSION>:<CANONICAL_ID>Include the same <variable> values discussed above.
View current ACLs
To view the current ACLs applied to a bucket or object, use the info commandReplace <acl-example> with the name of the target bucket and the object, if necessary.
s3cmd info s3://acl-exampleYou should see output like the following:
s3://acl-bucket-example/ (bucket):
   Location:  default
   Payer:     BucketOwner
   Expiration Rule: none
   Policy:    none
   CORS:      b'<CORSConfiguration xmlns="http://s3.amazonaws.com/doc/2006-03-01/"><CORSRule><AllowedMethod>GET</AllowedMethod><AllowedMethod>PUT</AllowedMethod><AllowedMethod>DELETE</AllowedMethod><AllowedMethod>HEAD</AllowedMethod><AllowedMethod>POST</AllowedMethod><AllowedOrigin>*</AllowedOrigin><AllowedHeader>*</AllowedHeader></CORSRule></CORSConfiguration>'
   ACL:       *anon*: READ
   ACL:       a0000000-000a-0000-0000-00d0ff0f0000: FULL_CONTROL
   URL:       http://us-east-1.linodeobjects.com/acl-example/
- The owner of the bucket always has the
full_controlpermission.- If you set an ACL that doesn't map to an ACL in Cloud Manager, it's displayed as
Custom.
Updated about 9 hours ago