Manage access keys
To start integrating Object Storage with your own applications, you need an access key. The access key provides access to buckets, and objects stored within those buckets. You can create several access keys, which lets you create a unique one for each application or user. When an application or user no longer requires access, you can revoke that access key without affecting any other application.
When an access key is generated, a corresponding secret key is also created. This secret key is used in tandem with the access key to authenticate connections. The secret key should not be shared.
Types of access keys
There are two types of access key:
| Type | Description |
|---|---|
| Unlimited access key | This is the default, when you create a new key. It gives you full access to all buckets on your account, in the regions you specify in the key. |
| Limited access key | When you're creating the key, you can enable this. It lets you set per-bucket permissions, which restrict the access key to a specific set of buckets and operations. Create these for users or applications that only need to perform certain kinds of actions. |
When determining which key type to use, consider these points:
- All access keys can create new buckets and list existing buckets. However, you can't perform other actions on a bucket using a limited access key.
- Once you've created an access key, you can't switch its type or modify per-bucket permissions on the access key.
- To apply bucket policies, you need to use an unlimited access key.
Limited access key permissions
You can apply these permissions to your buckets in each region you've enabled on the access key:
-
None. This restricts all access to the specified bucket. You can use the access key to view the bucket in the list of all buckets, but you can't access any objects stored in it.
-
Read (
read_only). You can list and retrieve all information about the specified bucket and objects stored in that bucket. This includes bucket metadata, object names, object metadata and contents (including non-current versions, if the bucket is versioned), and multipart upload information. You can also target these buckets as a source with a copy operation. -
Read/Write (
read_write). You can list, retrieve, add, delete, and modify most objects stored within the specified bucket. This includes everything that a read-only key can do in addition to modifying bucket metadata (with some exceptions), creating or overwriting objects, deleting objects, canceling multipart uploads, and modifying object metadata. You can also target these buckets as a destination for a copy operation.
Limited access keys are enforced through bucket policiesLimited access keys are enforced by provisioning a bucket policy on the selected buckets, aligning to the Read or Read/Write profiles. If you're using limited access keys and want to apply your own bucket policy on one of your buckets, you need to check whether a policy which manages access for a limited key already exists. If so, merge the existing policy into your changes before putting the new bucket policy on your bucket. If you don't merge the existing policy with the new policy, this will remove the permissions for the limited access key and will result in HTTP 403 errors when the limited access keys are used again in the future.
Supported S3 operations (by permissions)
| S3 operation | Read | Read/Write | Unlimited |
|---|---|---|---|
| AbortMultipartUpload | ✓ | ✓ | |
| CompleteMultipartUpload | ✓ | ✓ | |
| CopyObject (source) | ✓ | ✓ | ✓ |
| CopyObject (destination) | ✓ | ✓ | |
| CreateMultipartUpload | ✓ | ✓ | |
| DeleteBucketCors | ✓* | ✓* | |
| DeleteBucketLifecycle | ✓ | ✓ | |
| DeleteBucketPolicy | ✓ | ||
| DeleteBucketWebsite | ✓* | ✓* | |
| DeleteObject | ✓ | ✓ | |
| DeleteObjects | ✓ | ✓ | |
| DeleteObjectTagging | ✓ | ✓ | |
| GetBucketAcl | ✓ | ✓ | ✓ |
| GetBucketCors | ✓* | ✓* | ✓* |
| GetBucketLifecycle | ✓ | ✓ | ✓ |
| GetBucketLifecycleConfiguration | ✓ | ✓ | ✓ |
| GetBucketLocation | ✓ | ✓ | ✓ |
| GetBucketPolicy | ✓ | ✓ | ✓ |
| GetBucketVersioning | ✓ | ✓ | ✓ |
| GetBucketWebsite | ✓* | ✓* | ✓* |
| GetObject | ✓ | ✓ | ✓ |
| GetObjectAcl | ✓* | ✓* | ✓* |
| GetObjectLegalHold | ✓ | ✓ | ✓ |
| GetObjectLockConfiguration | ✓ | ✓ | ✓ |
| GetObjectRetention | ✓ | ✓ | ✓ |
| GetObjectTagging | ✓ | ✓ | ✓ |
| HeadBucket | ✓ | ✓ | ✓ |
| HeadObject | ✓ | ✓ | ✓ |
| ListBuckets | ✓ | ✓ | ✓ |
| ListMultipartUploads | ✓ | ✓ | ✓ |
| ListObjects | ✓ | ✓ | ✓ |
| ListObjectsV2 | ✓ | ✓ | ✓ |
| ListObjectVersions | ✓ | ✓ | ✓ |
| ListParts | ✓ | ✓ | ✓ |
| PutBucketAcl | ✓ | ||
| PutBucketCors | ✓* | ✓* | |
| PutBucketLifecycle | ✓ | ✓ | |
| PutBucketLifecycleConfiguration | ✓ | ✓ | |
| PutBucketPolicy | ✓ | ||
| PutBucketVersioning | ✓ | ✓ | |
| PutBucketWebsite | ✓* | ✓* | |
| PutObject | ✓ | ✓ | |
| PutObjectAcl | ✓* | ✓* | |
| PutObjectLegalHold | ✓ | ||
| PutObjectRetention | ✓ | ||
| PutObjectTagging | ✓ | ✓ | |
| UploadPart | ✓ | ✓ | |
| UploadPartCopy (source) | ✓ | ✓ | ✓ |
| UploadPartCopy (destination) | ✓ | ✓ |
*Only supported on E0 and E1 endpoint types.
Access key limits and quotas
See Per account quotas.
Manage access keys
Here are some common operations you can use to manage your keys.
View access keys
-
Log in to Cloud Manager.
-
Select the Object Storage link in the sidebar.
-
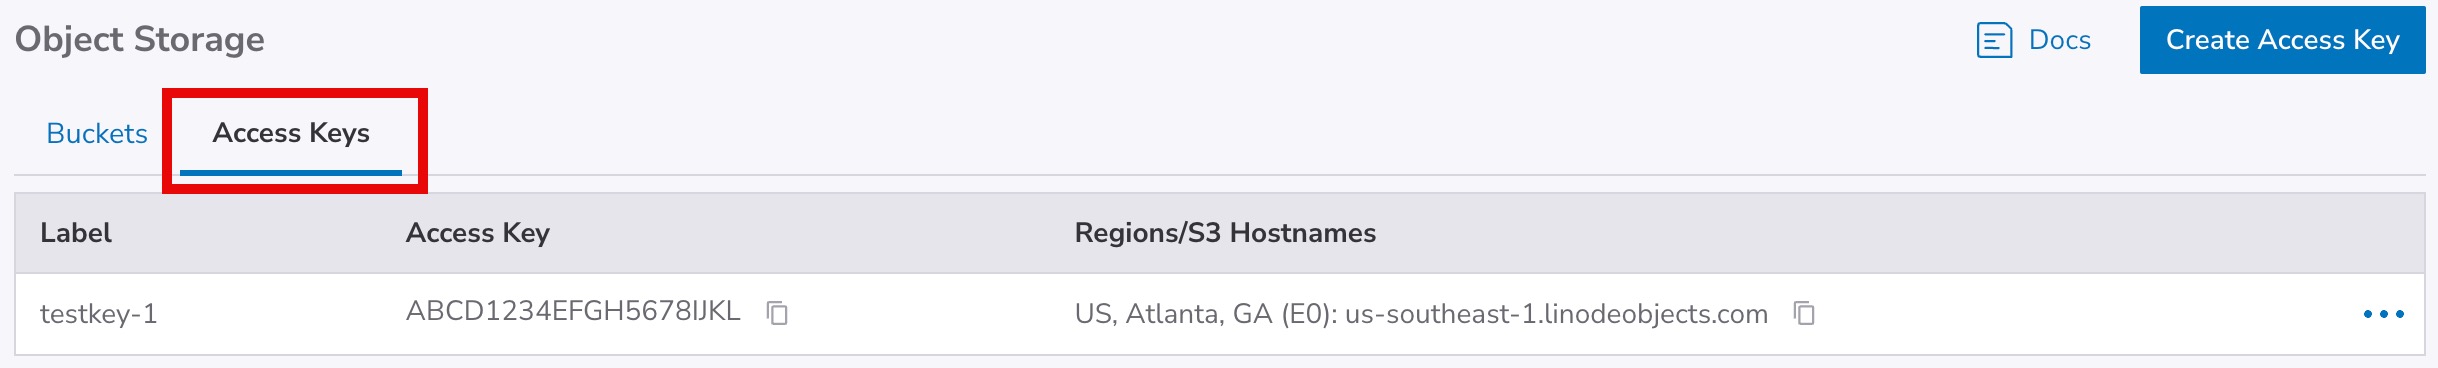
Select the Access Keys tab. All of the access keys added to your Object Storage account are listed.
Create an access key
-
Log in to Cloud Manager.
-
Select the Object Storage link in the sidebar.
-
Select the Access Keys tab. All of the access keys added to your Object Storage account are listed.
-
Select Create Access Key. The Create Access Key panel opens.
-
Enter a name (label) for the access key. This label is how you reference the access key in Cloud Manager and any Amazon S3-compatible client.
-
Select one or more Region where you want the key to have access.
-
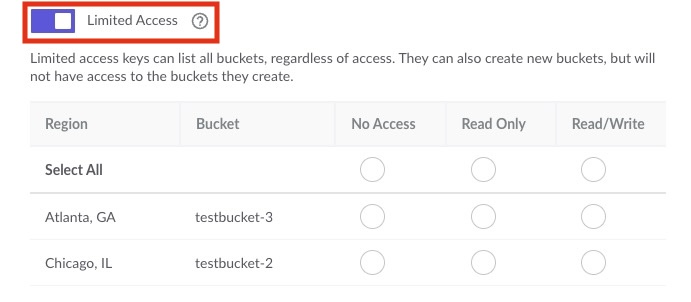
Enable the Limited Access switch to limit the permissions for the new access key on a per-bucket level.
-
Click the Create Access Key to finish the key. The Access Key window opens with specifics on your new key.
The Secret Key is only visible once in this window and can't view it again after you close this window. Store this secret key somewhere secure, such as a password manager.
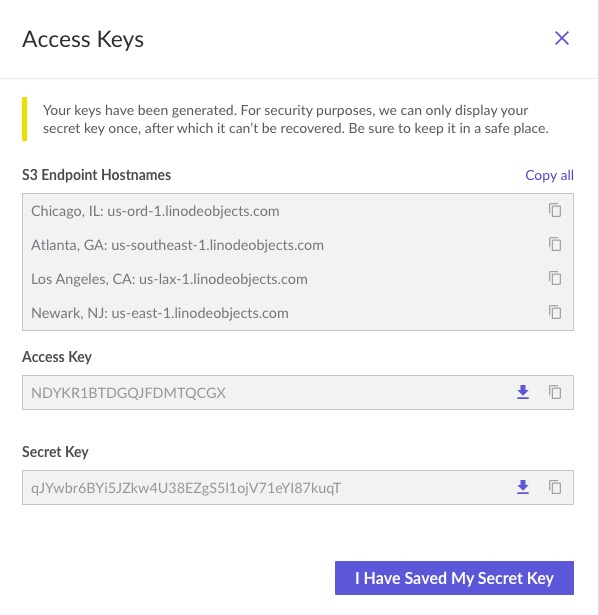
You now have the credentials needed to connect to Object Storage.
Revoke access key
When you revoke an access key, it's removed from your account and you can't use it to access applications that may have used it. Do this when decommissioning an application, ending a project with a third-party developer, or any other situation where an access key is no longer needed.
-
Log in to Cloud Manager.
-
Select the Object Storage link in the sidebar.
-
Select the Access Keys tab. All of the access keys added to your Object Storage account are listed.
-
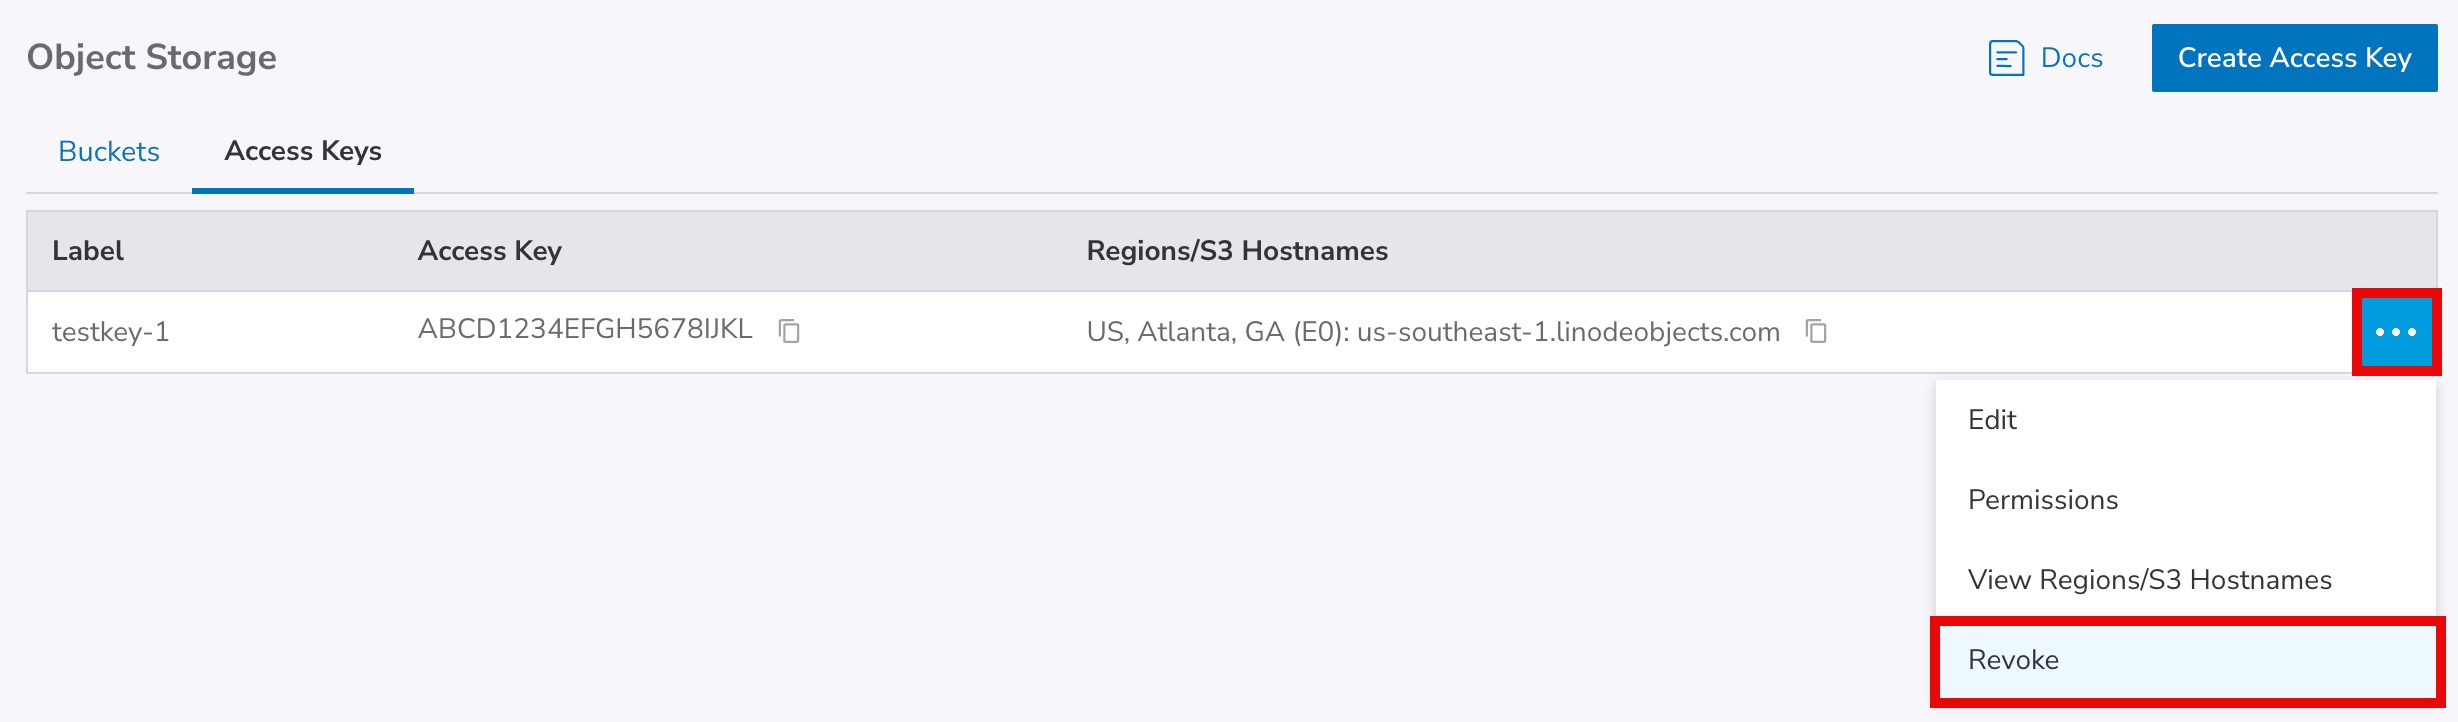
Locate the desired access key, click its ellipses, and select Revoke.
-
Click the Revoke button in the confirmation dialog to immediately revoke the access key.
Updated 11 days ago